
A fake Google password alert sent to a campaign chairman. A Word attachment opened by a clerk at a Ukrainian power company. Neither looked special when it arrived, and that is the point of studying examples of spear phishing: the dangerous email is usually dull. The cases below show the pretext, how it was delivered, and what the attacker did once someone clicked. If you need the short version of what does spear phishing mean first, it follows.
What is Spear Phishing?
Spear phishing is a phishing attack aimed at one person or one organization. A bulk phishing run sends the same fake parcel notice to everyone. In spear phishing, cybercriminals pick the recipient first and write for them, so the email mentions the invoice they are expecting or the manager they actually report to.
Typical sources are LinkedIn for reporting lines, press releases for project names, and stolen mail from a partner company for tone and signature blocks. The finished message usually poses as someone the target already trusts. Email is the main channel. Attackers also use LinkedIn messages, WhatsApp, Teams chats and phone calls, often in combination: an email followed by a call to “confirm” it.
Examples of Spear phishing attacks
Victims rarely publish full details of cybersecurity incidents, so the public record is patchy. These cases were reported in enough depth to learn from.
1. Operation Aurora (2009):
Operation Aurora was a run of targeted intrusions into large technology companies. Spear phishing was not the only technique in play, but it was how the attackers got their first foothold.
Selected employees received messages built to look routine, carrying a malicious link or attachment. One click was enough. The link led to a page that exploited a then-unknown flaw in Internet Explorer and dropped malware on the machine. From there the attackers moved inside the network toward source code repositories and other intellectual property.
Google, Adobe and Juniper Networks were among the named targets. Google went public about the intrusion, which is why the case is so well known. The attackers were widely believed to be state-sponsored, and the aim looked like espionage and theft of intellectual property rather than quick money.
2. Ukrainian Power Grid Attack (2015):
Here the phishing email was step one of a planned operation against Ukrainian electricity distributors. Staff at the power companies received emails with booby-trapped Office attachments. Opening one and enabling macros installed BlackEnergy malware on an office laptop.
That laptop was the way in. Over the following weeks the attackers worked their way from the corporate network to the systems that control substations, then opened breakers remotely. Thousands of people lost power. The lesson for defenders is uncomfortable: the email looked legitimate, the employee did a normal thing, and nothing stopped the next step. Blocking macros from internet files and separating office networks from control systems would have made the attackers’ job much harder.
3. Bengaluru-based Bank Heist (2016):
In 2016 a spear phishing attack hit the central bank of Bangladesh, and banks in India paid close attention. Attackers sent phishing emails to Bangladesh Bank employees and used that access to reach the bank’s SWIFT (Society for Worldwide Interbank Financial Telecommunication) environment and its credentials.
With those credentials they issued payment instructions that looked like genuine bank traffic, sending large sums to accounts in the Philippines and elsewhere. Some transfers were caught because of a spelling error in a beneficiary name; many were not. For Indian banks the takeaway was direct. The weak point was not SWIFT itself but the ordinary workstations and staff that had access to it, and those exist in every bank.
4. John Podesta Email Hack (2016):
John Podesta chaired Hillary Clinton’s 2016 presidential campaign. In March 2016 he got an email that looked like a Google security alert: someone had his password, and he should change it now. The button led to a fake Google sign-in page. His credentials were entered there, and the attackers had his password.
It worked because the pretext was one people see from Google all the time, and because the link sat behind a URL shortener, so the real destination was hidden. Investigators later attributed the operation to the Russian group known as Fancy Bear or APT28.
The attackers downloaded years of his mail. WikiLeaks published it during the 2016 U.S. presidential election, and the leak became a major political story. A hardware security key or app-based two-step check on the account would have made the stolen password close to useless.
5. Indian Tech Firms Targeted (2019):
In 2019, several Indian tech firms were reported as targets of a spear phishing campaign attributed to a Chinese hacking group. The emails went to specific employees and used themes that fit each person’s role, sometimes posing as a known organization. The likely goal was access to internal corporate data and intellectual property. Few details were made public, which is typical: most companies hit this way never say so.
Conclusion
Notice who got the email each time. Podesta had a mailbox full of campaign strategy. The Bangladesh Bank staff could reach SWIFT. The Aurora targets sat near source code, and the Ukrainian laptop sat on a network that led to substations. Attackers pick people by what their login can reach.
That tells you where to spend effort. Find the roles in your organisation with that kind of reach and give them training built on these exact pretexts, the fake Google alert and the macro attachment included. Send them simulated spear phishing so the first convincing lure they see comes from your team, not an attacker. Put security keys on their accounts. And write the playbook for a hijacked executive mailbox now: who resets credentials, who checks mail forwarding rules, who phones the bank to stop a payment.
FAQs
Here are the frequently asked questions about Examples of Spear Phishing.
What is a typical spear phishing attack?
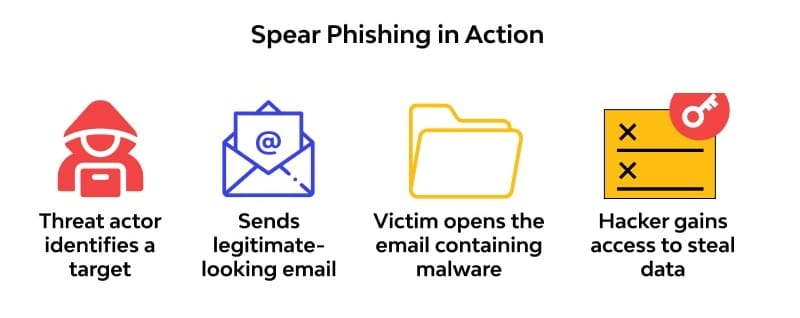
A typical spear phishing attack follows a set of steps, each carefully designed to trick a specific individual or organization into revealing sensitive information, such as login credentials or financial data.
What is a famous example of a phishing attack?
One of the most famous examples of a phishing attack is the “PayPal Phishing Scam” that occurred in 2011. In this incident, cybercriminals executed a large-scale phishing campaign targeting PayPal users. Here’s a summary of the attack:
Phishing Email:
Users received emails appearing to be from PayPal, claiming that there were security concerns with their accounts. The emails included urgent messages, warning users that their accounts would be suspended unless they took immediate action.
Fake Website:
The emails contained links that directed recipients to a fraudulent website designed to look exactly like the official PayPal login page. This fake website was created to trick users into entering their login credentials.
Credential Harvesting:
Once users entered their usernames and passwords on the fake website, the cybercriminals behind the phishing campaign harvested these credentials.
Unauthorized Access:
With the stolen login credentials, the attackers gained unauthorized access to users’ PayPal accounts. They could potentially make unauthorized transactions, access personal information, and misuse the compromised accounts.
Widespread Impact:
The phishing campaign had a widespread impact, affecting a large number of PayPal users. It garnered significant attention due to the scale of the attack and the potential financial losses for individuals.